How does your security compare with your industry? See it, area by area.
Answer guided questions online, at your own pace. Get maturity and risk scores for 11 security areas against an industry benchmark. Get a plan ranked by priority. Then we help you fix what it finds, with any vendor.
Three numbers your board understands. The detail your team needs.
- An executive summary in plain English
- Scores for 11 areas, such as Security Operations, Application Security and Network Security
- Findings by risk level, down to each of 75 capabilities
- Strategic actions with a priority, and a heatmap of where the work is
Built on NIST CSF 2.0: all six functions, from Govern to Recover. Maps to 17 of the 18 CIS Controls v8.
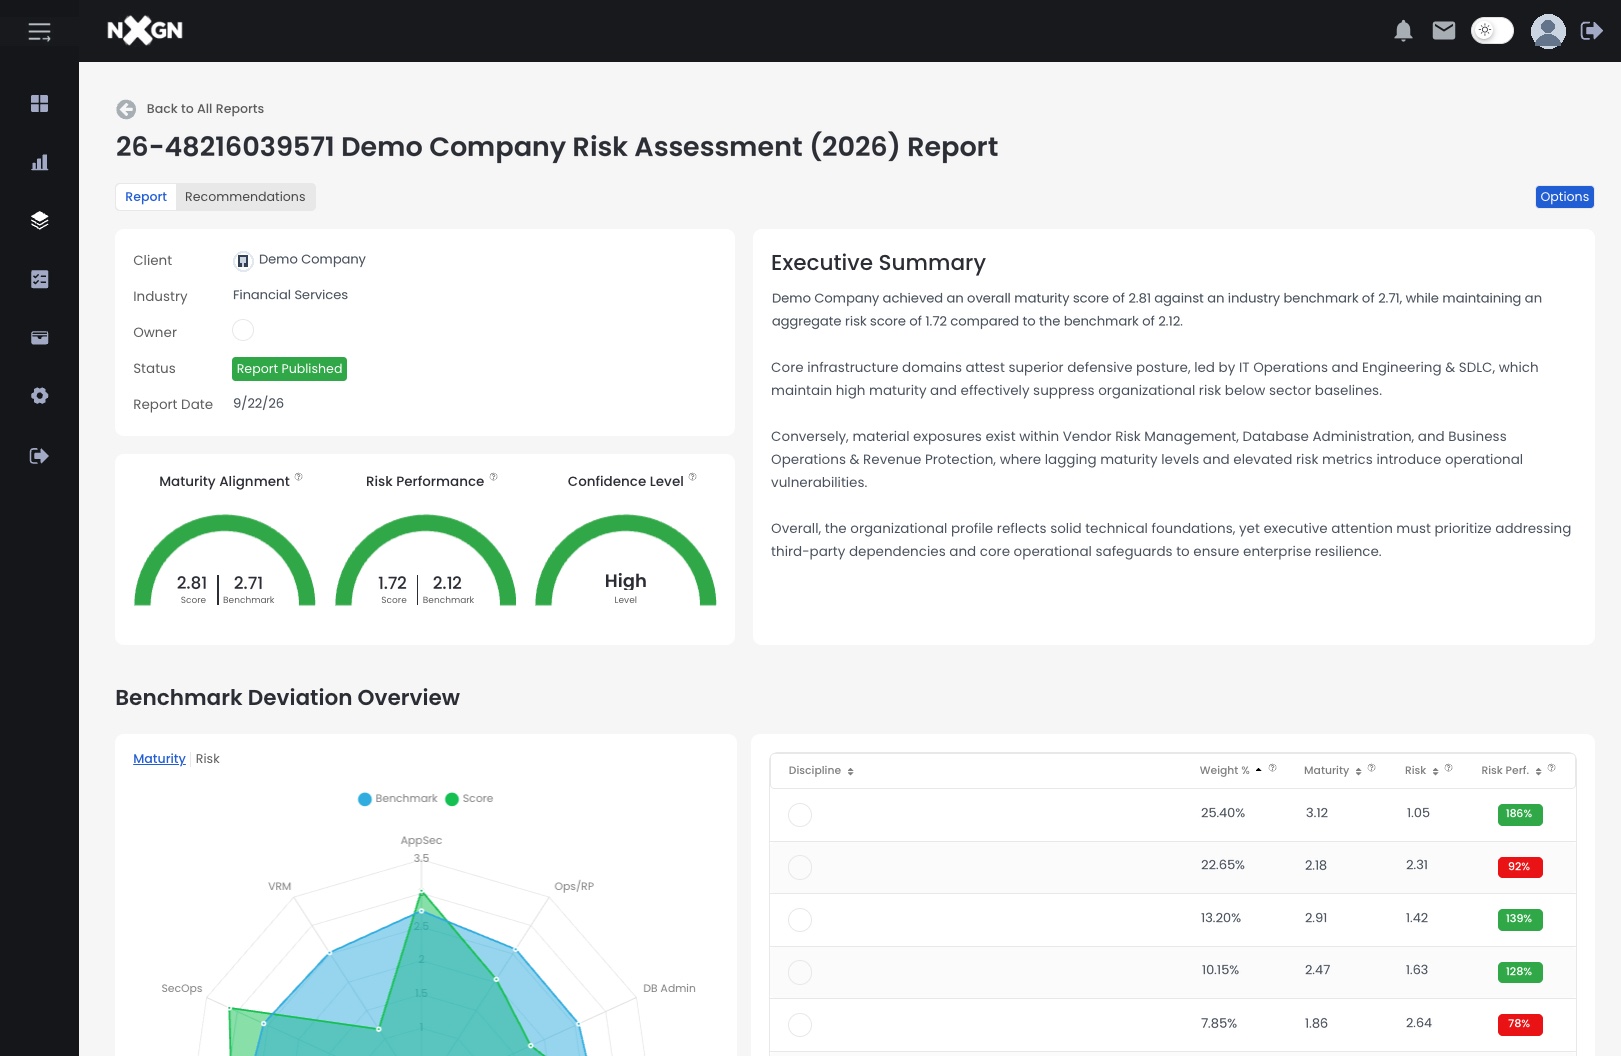
Real Hub screen. Client names, IDs and numbers are replaced.
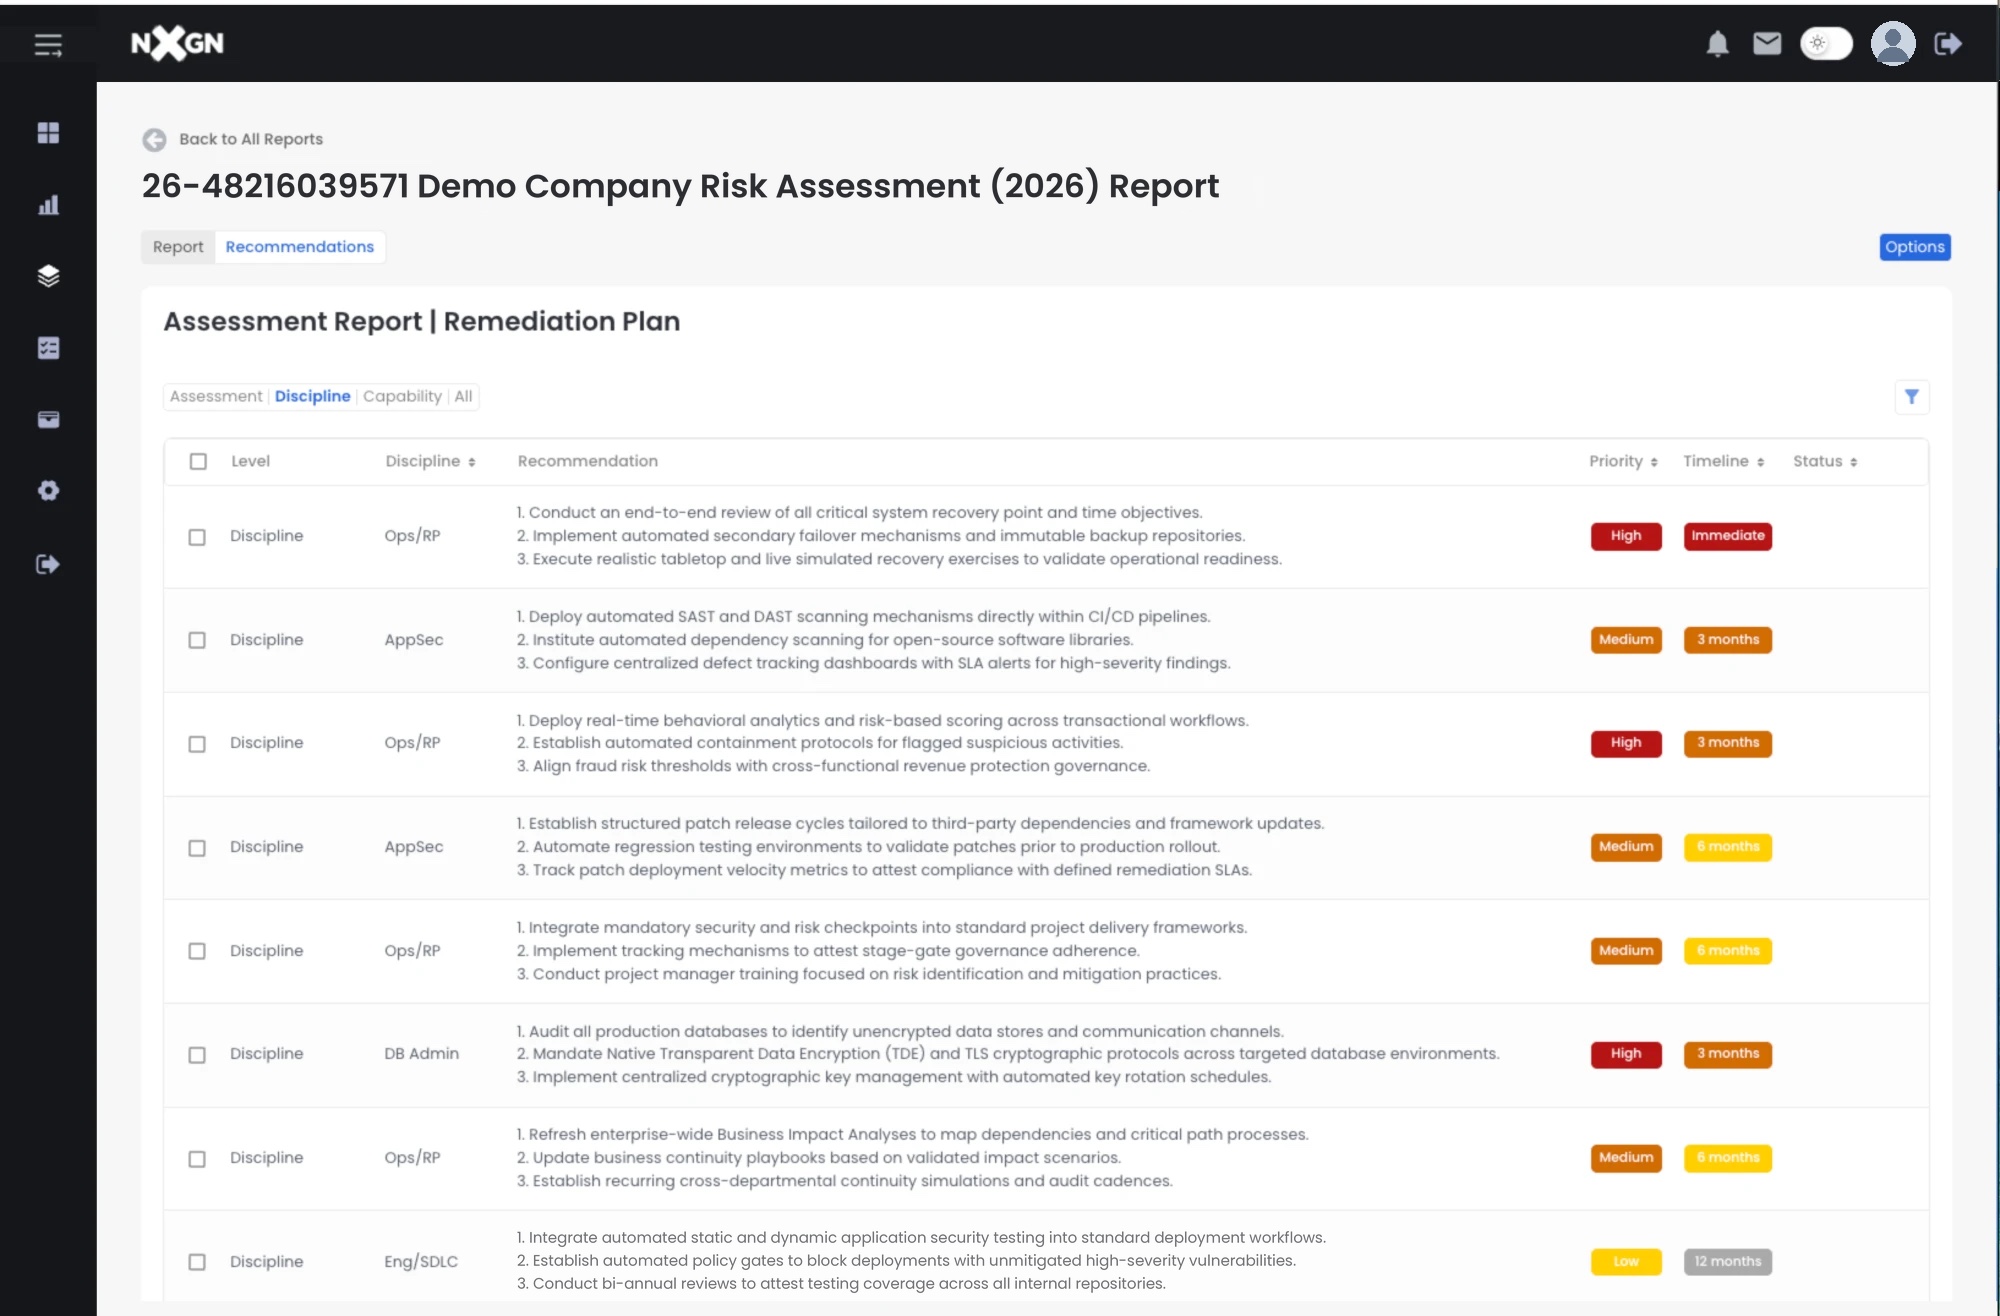
Real Hub screen. Client names, IDs and numbers are replaced.
See each area. Down to each capability.
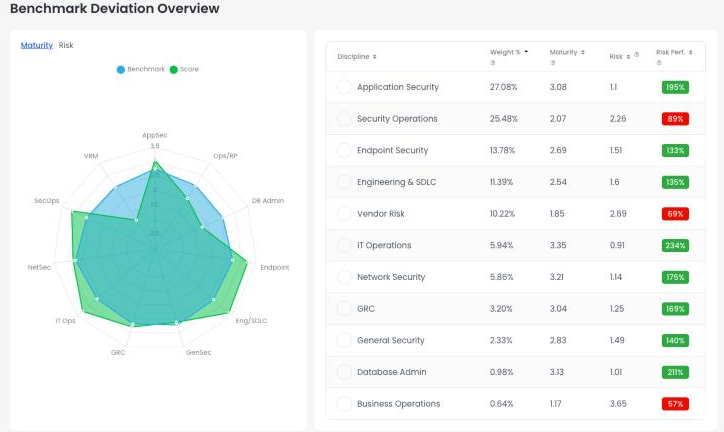
Benchmark table. Real Hub screen. Client name and all numbers are replaced.
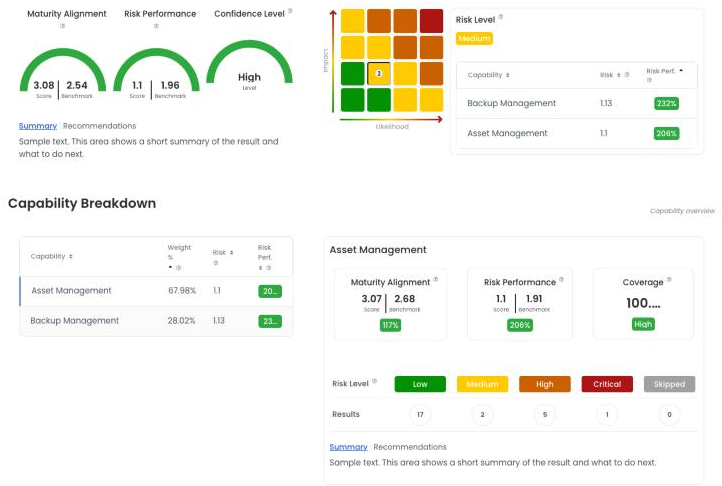
Area detail with capabilities. Real Hub screen. Numbers and text are replaced.
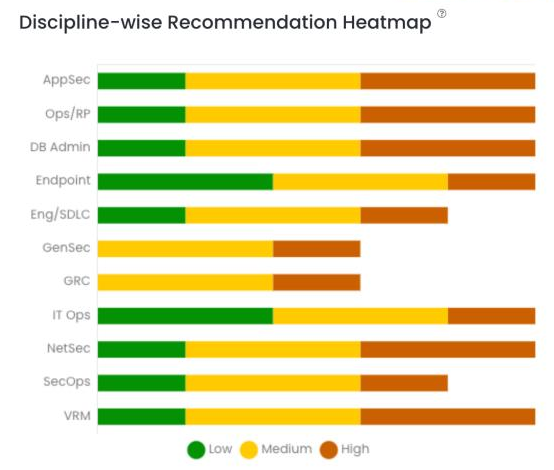
Recommendation heatmap. Real Hub screen.
Run it before someone asks. Not after.
Cyber insurance renewal
Know your gaps before the insurer's questionnaire does.
A list of gaps to close, ranked by risk
Board or audit meeting
Show where you stand against your industry, in three numbers.
An executive summary for the board pack
A new security or IT lead
Get a baseline in the first weeks, before any spend decision.
A baseline to measure progress against
Budget planning
Put next year's money where the risk is highest.
Actions ranked by priority
Answer. See the scores. Get the plan.
No software to install and no access to your systems. You answer, and the report uses your answers.
Answer guided questions
- About your controls and how you run security
- Multiple choice. Each answer describes a level of practice.
- Assign questions to colleagues and see progress
- Save and come back later
See the scores
- 11 areas, each with a weight
- Each area against your industry benchmark
- The benchmark comes from AI research of practice in your industry
Get the plan
- Recommendations with a priority and a timeline
- Subscribe to track your scores over time
A report is a start. We help you finish.
The same NXGN team takes you from the plan to the fix. Each fix can use any vendor, or the tools you already own.
- Since 2012Based in Lisle, Illinois
- 100% founder-ownedNo outside investors to answer to
- Inc. 5000Inc. 5000 honoree, four years in a row
- About 2,470 solutionsin 195 categories in our Solutions Hub
- 60+ enterprise clientsMost of them Fortune 2000
A security vendor's assessment leads to its own tool. Ours leads to your best option.
A neutral plan
We do not make the tools that the plan recommends. "Use what you already own" is a real answer.
Evaluate freely
If you need a new tool, talk to any vendor through us. We share no name and no client details while you explore.
One team, report to fix
The advisor who reads your report with you also runs the next step.
Is this a pen test?
No. The assessment uses your answers about how you run security. It does not test your systems. A pen test is the next step when you need proof of what an attacker can reach.
Who sees our answers?
Your answers and your report are visible only to your company and your NXGN team. We never sell or share them.
Is AI trained on our data?
AI writes the summaries from your own answers. Your data is not used to train outside models.
How long does it take?
It is self-paced. You can save and come back later. You can assign questions to colleagues and see progress.
Which framework is it based on?
Built on NIST CSF 2.0: all six functions, from Govern to Recover. Maps to 17 of the 18 CIS Controls v8.
How is the benchmark made?
AI researches security practice in your industry. We use that research as a benchmark for comparison. It is not a survey of other companies.
Which areas does it cover?
It covers 11 areas: Engineering & SDLC; IT Operations; Security Operations; Application Security; Network Security; Governance, Risk & Compliance; Endpoint Security; Database Administration; Vendor Risk Management; General Security; and Business Operations & Revenue Protection. AI safety and governance comes next.
What does it cost?
Ask us. It is a paid subscription.
 Start here
Know where you stand before your next renewal.
A short call with an NXGN advisor. We set up your assessment and read the report with you.
Pricing: ask us.